
Trading bots are convenient because they hold a key and sign for you. That is also why they get drained. The safest setup treats the bot wallet as a hot wallet you expect could be lost: fund it with a trading float only, cap what it can do, keep approvals narrow and move profits out regularly. Teams building bots need the mirror image: protected keys, delays and limits on withdrawals, tightly scoped router approvals, monitoring, and a refund plan written before anything goes wrong.
This checklist is anchored in three real incidents and in what 2026 has added to the threat picture.
What past bot incidents teach
| Incident | What went wrong | Reported loss | Response |
|---|---|---|---|
| Maestro, 24 Oct 2023 | A flaw in a new version of the Router2 contract let anyone make the router perform arbitrary calls. The attacker used transferFrom to pull tokens from wallets that had approved the router. |
Over 280 ETH, about $485,000 to $500,000 | Router logic replaced about 30 minutes after discovery. Maestro said refunds cost 610 ETH: 276 ETH buying back tokens and 334 ETH paid in ETH plus a 20% top-up for two illiquid tokens. CertiK counted 106 affected addresses. |
| Banana Gun, 19 Sep 2024 | Banana Gun said a potential vulnerability in the Telegram message oracle it used "may have led to the exploit". Transfers out of victims' bot wallets appeared to be executed manually. | Early community estimates 563 ETH (about $1.4m); Banana Gun later put it at about $3m across 11 users | Bots shut down and patched within a day. Full refund from the treasury. Added a two-hour delay on transfers, 2FA for transfers and audits of back end and front end. |
| Bloom, 26 Oct 2026 | Bloom blamed a remote code execution flaw in a third-party module and said no private keys were compromised. Bitquery said each drain was signed with the wallet's private key; the discrepancy is unresolved. | About $950,000 in SOL from roughly 48 wallets of nine users, in 94 seconds | Full reimbursement pledged. Five of the drained wallets had been inactive on the bot since the first half of 2025. |
Three patterns stand out:
- Approvals outlive their purpose. Maestro's victims lost tokens because of approvals they had granted to the router. Revoke.cash still lists the exploit and notes that users stay exposed until they revoke.
- The weak link is often around the bot, not in it. A messaging oracle at Banana Gun and a third-party module at Bloom: the attack surface includes everything the bot depends on.
- Dormant wallets are still live wallets. Bloom's drained wallets included ones nobody had used in over a year.
All three teams refunded or pledged to refund users, and that shaped how users judged them afterwards. Our earlier pieces on sniper bots' risks and Banana Gun in numbers give background on how these products work.
What changed in 2026
Two developments raise the stakes.
EIP-7702 delegation. Since Ethereum's Pectra upgrade in May 2025, an ordinary wallet can sign an authorization that makes it run a smart contract's code. The delegation persists until it is changed. Cointelegraph reported that Wintermute found in May 2025 that most early delegations pointed to malicious "sweeper" contracts. In September 2025, World Liberty Financial token holders reported losses tied to malicious delegations. The EIP itself says applications "must not expect that they can suggest the user sign an authorization". Any bot, website or "migration tool" asking you to sign one is a red flag.
Signing systems as the target. On 29 October 2026 Binance lost about $6.36 billion, by TRM Labs' count, after attackers got its hot wallet signing system to sign transfers and, on Ethereum, 50 EIP-7702 authorizations. We covered the details in our Binance analysis. A trading bot is a small version of the same thing: a service that signs on your behalf. If an attacker controls what it is told to sign, the key's safety does not matter.
Checklist for traders
Wallets and balances
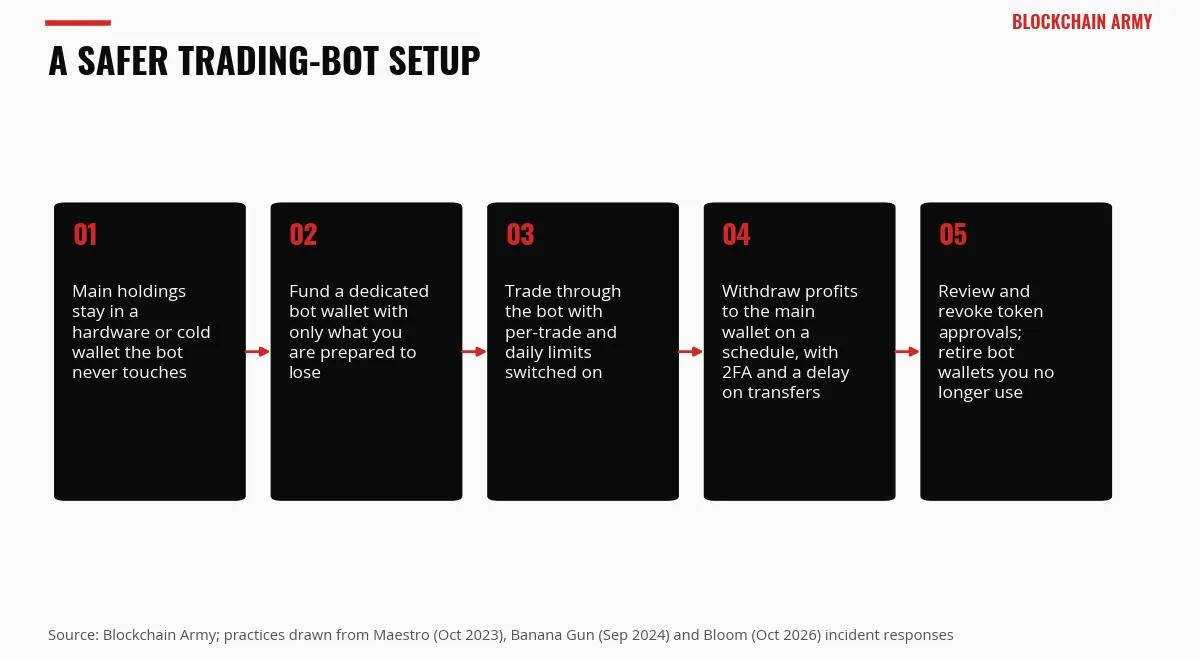
- Use a dedicated wallet for each bot. Never import your main wallet's seed phrase or private key into a bot.
- Keep only a trading float in it, sized to what you can afford to lose today.
- Sweep profits to a hardware or cold wallet on a fixed schedule. See our guide to hardware wallets.
- Empty and retire bot wallets you no longer use. Dormant does not mean safe.
- If you export a bot's private key to use elsewhere, treat that wallet as compromised from then on.
Limits and confirmations
- Turn on every limit the bot offers: max buy size, max slippage, daily spend.
- Enable 2FA or withdrawal confirmations, and transfer delays if available.
- Protect the Telegram account itself: two-step verification password, no session on shared devices, and review active sessions regularly.
Approvals and signatures
- Review token approvals monthly with a tool such as Revoke.cash and revoke ones you no longer need, especially unlimited approvals to old routers.
- Never sign an EIP-7702 authorization or an unfamiliar "upgrade your wallet" request from a bot, link or support DM.
- Read what your wallet shows before signing. If it cannot decode the request, do not sign it.
Links and impersonation
- Reach the bot only through the handle and link on the project's official website or verified X account. Bookmark it.
- Assume any DM offering support, airdrops or "bot upgrades" is a scam.
- Check the bot's track record: published audits, incident history, and whether it repaid users last time.
Checklist for teams building bots
| Area | Minimum standard |
|---|---|
| Key management | User keys encrypted at rest, with decryption in an HSM, MPC or enclave-backed service, not in application memory on a general server. No plaintext keys in logs, backups or support tools. |
| Signing policy | A separate policy service decodes every transaction before signing. It refuses EIP-7702 authorizations, unknown contract calls and transfers outside the user's own settings. |
| Withdrawals | Confirmation via a second factor, a time delay on external transfers (Banana Gun added two hours), and a delay on changing withdrawal addresses. |
| Rate limits | Per-user and global caps on outflows per minute and per hour, with an automatic pause on spikes. Bloom's drain took 94 seconds; limits must work at machine speed. |
| Router contracts | Minimal and immutable where possible. No arbitrary-call paths. Approvals scoped to exact amounts or Permit2-style expiring allowances, never "unlimited by default". Audit every new router version before release; Maestro's flaw shipped in an upgrade. |
| Dependencies | Inventory every third-party module, oracle and library. Pin versions, review updates, and isolate them from key material. |
| Monitoring | Alerts on unusual transfer patterns, mass outflows, new approval targets and dormant-wallet activity. A kill switch someone can reach at 3am. |
| Bug bounty | A public program with clear scope and payout, so researchers report to you rather than exploit you. |
| Incident and refund policy | A written plan: who pauses the bot, who communicates, how losses are assessed, and which reserve pays refunds. Publish the policy before you need it. |
Two of these deserve emphasis. First, approval scoping: Maestro's router could move victims' tokens only because they had granted it approvals. A router that requests exact-amount or expiring allowances limits the damage of any future bug. Second, the refund reserve: Maestro, Banana Gun and Bloom all made users whole or pledged to. A treasury that can do that without selling the project token is part of a bot's security model. Banana Gun specifically said no tokens would be sold to fund its reimbursements.
For architecture background, see our guide on how to build a crypto trading bot. If you need router contracts or a signing-policy layer built and reviewed, that falls under our custom smart contract development work.
The short version
For traders: separate wallets, small floats, limits on, approvals revoked, never sign an authorization you did not seek out. For builders: protect keys, verify what you sign, slow down withdrawals, scope approvals, watch everything, and have the refund money ready. None of this is new. The 2026 incidents show what it costs to skip it.
Sources
- The Block — Maestro Telegram bot suffers a contract exploit: $500,000 of ETH stolen
- Cointelegraph — Telegram trading bot Maestro refunds users 610 ETH after router exploit
- Revoke.cash — Maestro exploit
- The Block — Banana Gun team investigates reports of user wallets being drained, Telegram bot offline
- The Block — Banana Gun promises to refund $3 million stolen from impacted users
- Cointelegraph — Bloom bot hackers took $953K faster than you can make popcorn
- Cointelegraph — EIP-7702 didn't cause Binance hack, but may have amplified losses
- TRM Labs — North Korea steals USD 6.36 billion from Binance in the largest hack in history
- Ethereum Improvement Proposals — EIP-7702: Set Code for EOAs
How we research, write and fact-check: Editorial & AI policy.
Disclaimer: this article is for informational and educational purposes only and does not constitute financial, investment, legal or tax advice. Crypto-assets are volatile and high-risk: always do your own research (DYOR) and consult a qualified professional before making any decision. Not financial advice.